AI Agent Security Runtime Controls
Secure agents against prompt injection with MCP/tool and runtime controls.
Primary Paths
All AI Engineering
Browse the complete reviewed English AI engineering library.
Agent Security Auditor
Scan Agent/MCP configuration and code in-browser for shell, secret, permission, retention, third-party and runtime-control risks without uploading your configuration.
Agent Side-Effect Evaluator
Verify real terminal state and side effects instead of trusting final-answer fluency or well-formed tool calls.
AI Agent Security Guide
Connect prompt injection, MCP/tool permissions, identity, memory, sandboxing and runtime controls into one production defense model.
Tool Authorization Policy Gate
Re-check identity, tenant, resource, scope, arguments and approval at tool execution time.
MCP Security Best Practices
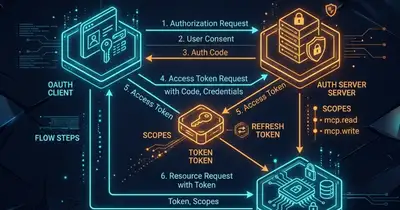
Treat MCP servers, tool descriptions, authorization and remote integrations as real third-party execution boundaries.
MCP Configuration Security Audit
Check actual secrets, shell and remote MCP permissions after reviewing tool-poisoning and supply-chain risks.
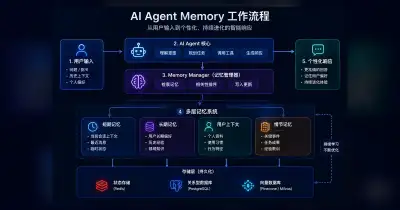
Memory & Multi-Agent Trust
Protect persistent memory and inter-agent handoffs with provenance, scope isolation, validation, delegated authorization and replay-aware controls.
MCP Server Production Governance
Review third-party server lifecycle, governance and runtime controls after the configuration audit.
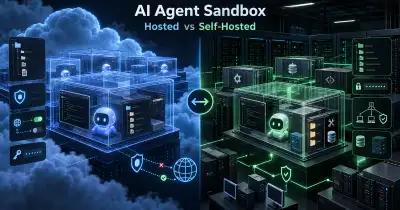
MCP Sandbox Architecture
Constrain code execution, filesystem access and network egress so agent mistakes cannot freely escape the execution boundary.
OpenAI Zero Data Retention for AI Agents
Map ZDR across Responses API, remote MCP, prompt caching, memory, audit and Data Residency.